


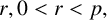


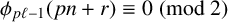



1 Introduction
In his 1984 American Mathematical Society memoir [Reference Andrews1], George Andrews defined two families of combinatorial objects known as generalised Frobenius partitions. These are generalisations of the two-rowed arrays, often known as Frobenius symbols, which arise from considering the rows and columns of the Ferrers graph of an ordinary partition once the main diagonal has been ‘removed’. In the process, Andrews defined two families of functions,
 $\phi _k(n)$
and
 $c\phi _k(n),$
as the number of generalised Frobenius partitions of weight n in these two families of objects. In [Reference Andrews1], Andrews studied
 $\phi _k(n)$
and
 $c\phi _k(n)$
from several perspectives, including proving a number of Ramanujan-like congruences satisfied by these functions. This, in turn, led a number of others to extend Andrews’ congruence results.
While there exists an extensive literature on the subject of congruences satisfied by generalised Frobenius partition functions, our focus in this note will be on parity results. We highlight here that a number of authors have proven congruence results with even moduli for these functions (see, for example, Andrews [Reference Andrews1, Theorem 10.2], Baruah and Sarmah [Reference Baruah and Sarmah2, Reference Baruah and Sarmah3], Chan et al. [Reference Chan, Wang and Yang4], Cui and Gu [Reference Cui and Gu5], Cui et al. [Reference Cui, Gu and Huang6] and Jameson and Wieczorek [Reference Jameson and Wieczorek9]). Several additional papers involving congruence results for generalised Frobenius partitions, but with odd moduli, also appear in the literature.
What is striking about many of the works cited above is that the authors focus specifically on a particular value of the parameter k in order to manipulate the generating function in question to prove their results. One exception is the following result of Andrews.
Theorem 1.1 [Reference Andrews1, Theorem 10.2].
Let p be prime and let r be an integer such that
 $0<r<p.$
For all
 $n\geq 0,$
 $$ \begin{align*}c\phi_p(pn+r) \equiv 0 \pmod{p^2}.\end{align*} $$
Another exception to focusing on a particular value of the subscript k is the following result of Garvan and Sellers.
Theorem 1.2 [Reference Garvan and Sellers7, Theorem 2.2].
Let p be prime and let r be an integer such that
 $0<r<p.$
If
 $$ \begin{align*} c\phi_k(pn+r) \equiv 0 \pmod{p} \end{align*} $$
for all
 $n\geq 0,$
then
 $$ \begin{align*} c\phi_{pN+k}(pn+r) \equiv 0 \pmod{p} \end{align*} $$
for all
 $N\geq 0$
and
 $n\geq 0.$
Our goal in this note is to follow a path similar to the above theorem of Garvan and Sellers, where an infinite family of values of k is identified while the value of the modulus is fixed.
It is clear, when one reviews the literature on the subject of congruences satisfied by generalised Frobenius partition functions, that the functions
 $c\phi _k(n)$
satisfy many more congruences than their counterpart functions
 $\phi _k(n).$
One might argue that this is true ‘combinatorially’ given the structure of the objects being counted by these functions (and symmetries that are inherent in the two-rowed arrays counted by
 $c\phi _k(n)$
). It is also true that, although the generating functions for each of these two families of functions are extremely similar, the presence of certain powers of roots of unity in the generating function for
 $\phi _k(n),$
and the corresponding absence of such roots of unity in the generating function for
 $c\phi _k(n),$
may contribute to the relative lack of congruences satisfied by
 $\phi _k(n).$
Whatever the case, our primary goal in this note is to alter this narrative by proving the following surprising result.
Theorem 1.3. Let
 $\ell $
be a positive integer,
 $p\geq 5$
be prime and let
 $r, 0< r < p,$
be an integer such that
 $24r+1$
is a quadratic nonresidue modulo
 $p.$
For all
 $n\geq 0,$
 $$ \begin{align*} \phi_{p\ell-1}(pn+r) \equiv 0 \pmod{2}. \end{align*} $$
2 Proof of Theorem 1.3
In order to prove Theorem 1.3, we need a few preliminary facts. First, we remind the reader of the q-Pochhammer symbol
 $(A;q)_\infty $
which is defined as follows:
 $$ \begin{align*}(A;q)_\infty = (1-A)(1-Aq)\cdots(1-Aq^{n})\cdots.\end{align*} $$
We will also need the following two well-known results.
Theorem 2.1. We have
 $$ \begin{align*} (q;q)_\infty = \sum\limits_{k = -\infty}^\infty (-1)^k q^{{(3k^2-k)}/{2}}. \end{align*} $$
Proof. See Hirschhorn [Reference Hirschhorn8, (1.6.1)].
Theorem 2.2. We have
 $$ \begin{align*} (q;q)_\infty^3 = \sum\limits_{k=0}^\infty (-1)^k(2k+1)q^{{(k^2+k)}/{2}}. \end{align*} $$
Proof. See Hirschhorn [Reference Hirschhorn8, (1.7.1)].
Next, we prove an extremely important fact about the generating function for
 $\phi _k(n)$
for all
 $k\geq 1$
using a key result that appears in Andrews [Reference Andrews1].
Theorem 2.3. Let
 $$ \begin{align*} \Phi_k(q) = \sum_{n=0}^\infty \phi_k(n)q^n \end{align*} $$
be the generating function for the generalised Frobenius partition function
 $\phi _k(n).$
Then
 $$ \begin{align*} \Phi_k(q) \equiv \frac{(q;q)_\infty}{(q^{k+1};q^{k+1})_\infty} \pmod{2}. \end{align*} $$
Proof. From Andrews’ memoir [Reference Andrews1, Theorem 7.1],
 $$ \begin{align*} \Phi_k(q) = \frac{1}{ (q;q)_\infty^2(q^{k+1};q^{k+1})_\infty}\sum_{\substack{j,r = -\infty\\ r \geq (k+1)|j|}}^{\infty}(-1)^{r+kj}q^{\binom{r+1}{2}-\binom{k+1}{2}j^2}. \end{align*} $$
Therefore,
 $$ \begin{align*} \Phi_k(q) &= \frac{1}{ (q;q)_\infty^2(q^{k+1};q^{k+1})_\infty}\sum_{\substack{j,r = -\infty\\ r \geq (k+1)|j|}}^{\infty}(-1)^{r+kj}q^{\binom{r+1}{2}-\binom{k+1}{2}j^2}\\[3pt] &= \frac{(q;q)_\infty}{ (q;q)_\infty^3(q^{k+1};q^{k+1})_\infty}\sum\limits_{r =0}^\infty q^{\binom{r+1}{2}} \sum\limits_{|j|\leq r/(k+1)}(-1)^{r+kj}q^{-\binom{k+1}{2}j^2} \\[3pt] &\equiv \frac{(q;q)_\infty}{ (q;q)_\infty^3(q^{k+1};q^{k+1})_\infty}\sum\limits_{r =0}^\infty q^{\binom{r+1}{2}} \sum\limits_{|j|\leq r/(k+1)}q^{-\binom{k+1}{2}j^2} \pmod{2} \\[3pt] &= \frac{(q;q)_\infty}{ (q;q)_\infty^3(q^{k+1};q^{k+1})_\infty}\sum\limits_{r =0}^\infty q^{\binom{r+1}{2}}\bigg(1+2 \sum\limits_{1\leq j \leq r/(k+1)}q^{-\binom{k+1}{2}j^2} \bigg) \\[3pt] &\equiv \frac{(q;q)_\infty}{ (q;q)_\infty^3(q^{k+1};q^{k+1})_\infty}\sum\limits_{r =0}^\infty q^{\binom{r+1}{2}} \pmod{2} \\[3pt] &\equiv \frac{(q;q)_\infty(q;q)_\infty^3}{ (q;q)_\infty^3(q^{k+1};q^{k+1})_\infty} \pmod{2} \\[3pt] \end{align*} $$
thanks to Theorem 2.2. The result follows immediately.
We are now in an excellent position to prove Theorem 1.3.
Proof of Theorem 1.3.
Thanks to Theorem 2.3, we know that the generating function for
 $\phi _{p\ell -1}$
satisfies
 $$ \begin{align*} \sum_{n=0}^\infty \phi_{p\ell-1}(n)q^n &\equiv \frac{(q;q)_\infty}{(q^{p\ell};q^{p\ell})_\infty} \pmod{2} \\ &\equiv \frac{1}{(q^{p\ell};q^{p\ell})_\infty} \sum\limits_{k = -\infty}^\infty q^{({3k^2-k})/{2}} \pmod{2} \end{align*} $$
where the last statement follows from Theorem 2.1. Since
 $(q^{p\ell };q^{p\ell })_\infty $
is a function of
 $q^p,$
and since we are interested in the parity of the values
 $\phi _{p\ell -1}(pn+r)$
where
 $0<r<p,$
we simply need to determine when
 $$ \begin{align*}pn+r = \frac{3k^2-k}{2}\end{align*} $$
for some integer
 $k.$
After completing the square, this is equivalent to asking whether
 $$ \begin{align*} 24r+1 & \equiv 36k^2-12k+1 \pmod p \\ & \equiv (6k-1)^2 \pmod p \end{align*} $$
However, we assumed that
 $24r+1$
is a quadratic nonresidue modulo p in the statement of this theorem. Therefore,
 $pn+r$
can never be represented as
 $(3k^2-k)/2$
for any integer k. This implies that
 $$ \begin{align*} \phi_{p\ell-1}(pn+r) \equiv 0 \pmod{p}.\\[-2.7pc] \end{align*} $$
3 Concluding remarks
It should be noted that a companion result to Theorem 1.3 exists for the functions
 $c\phi _k(n)$
(which is not at all surprising).
Theorem 3.1. For all
 $k\geq 1$
and all
 $n\geq 0,$
 $$ \begin{align*} c\phi_{2k}(2n+1) \equiv 0 \pmod{2}. \end{align*} $$
In a real sense, the proof of this result already appears in the literature (see, for example, Garvan and Sellers [Reference Garvan and Sellers7] as well as Baruah and Sarmah [Reference Baruah and Sarmah3]). For completeness, we provide a proof here.
Proof. The generating function for
 $c\phi _{2k}(n),$
as provided by Andrews [Reference Andrews1], is the constant term in
 $$ \begin{align*} CG_{2k}(z) = \prod_{n=0}^\infty(1+zq^{n+1})^{2k}(1+z^{-1}q^n)^{2k}. \end{align*} $$
Thanks to the binomial theorem,
 $$ \begin{align*} CG_{2k}(z) &= \prod_{n=0}^\infty(1+zq^{n+1})^{2k}(1+z^{-1}q^n)^{2k}\\ & \equiv \prod_{n=0}^\infty(1+z^2q^{2n+2})^{k}(1+z^{-2}q^{2n})^{k} \pmod{2}. \end{align*} $$
The theorem follows immediately because the last product is a function of
 $q^2.$



