


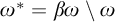


1 Introduction
Topological semantics appeared as one of the first semantics for both intuitionistic logic
 $\mathbf {IL}$
and modal logic
 $\mathbf {S4}$
. First, in 1938, Tarski, in his pioneering work [Reference Tarski15], proved that
 $\mathbf {IL}$
is complete with respect to all topological spaces (propositions are interpreted as open sets). He also obtained the remarkable result that any dense-in-itself separable metrizable space (e.g., the Cantor space
 $\mathbb {C}$
or the real line
 $\mathbb {R}$
), is complete for
 $\mathbf {IL}$
. Later in 1944 he and McKinsey in their famous paper [Reference Tarski and McKinsey16] proved an analogous results for the modal logic
 $\mathbf {S4}$
. Finally, assuming AC, the requirement of separability in the metrizable case was proved redundant by Rasiowa and Sikorski in [Reference Rasiowa and Sikorski13].
Recently in [Reference Bezhanishvili and Harding4] G. Bezhanishvili and J. Harding described logical counterparts of the important spaces
 $\beta \omega $
and
 $\omega ^*$
, which turned out to correspond to modal logics
 $\mathbf {S4.1.2}=\mathbf {S4}+\Box \Diamond \varphi \leftrightarrow \Diamond \Box \varphi $
and
 $\mathbf {S4}$
respectively. However their proof needed the additional assumption beyond ZFC that
 $\mathfrak {a=c}$
, i.e. the statement that every infinite maximal almost disjoint family of subsets of
 $\omega $
has cardinality continuum. The main part of the proof of the completeness theorem resides in proving that there exists a surjective interior map from
 $\beta \omega $
(resp.
 $\omega ^*)$
onto any finite tree with an additional top element (resp. any finite tree) where the topology of the target space is the upset topology. Additionally one also needs to guarantee that the fibers of the map are crowded in βω ∖ ω.
In this paper we improve their results by weakening the assumption
 $\mathfrak {a=c}$
to the assumption that there is a completely separable maximal almost disjoint family of subsets of
 $\omega $
. This assumption follows from
 $\mathfrak {a=c}$
but it is much weaker. It should be noted here, that it is in fact a long standing open question whether the existence of such a family can perhaps be proved in ZFC alone. The idea behind our proof is the same as the one in [Reference Bezhanishvili and Harding4], i.e. we also construct a surjective interior map, however, our construction is simpler and only relies on the existence of a completely separable MAD family.
The content of this paper is organized as follows: in the preliminary section we recall basic notions concerning modal logics and their topological completeness. We then describe the so called interior map strategy (see also [Reference Bezhanishvili and Harding4]) which we use to prove the main completeness theorems. The introductory part is concluded by recalling some basic facts about the topology of
 $\beta \omega $
and almost disjoint families. In the third section we construct the interior map and then we use this map in the last section to prove the main completeness results.
2 Preliminaries
Modal logics are presented using the standard modal language which consists of connectives of classical logic, a unary connective
 $\Box $
expressing necessity and a countable set of variables. We consider the
 $\Diamond $
connective to be shorthand for
 $\Diamond \varphi =_{\textit{df}} \neg \Box \neg \varphi $
. The collection of all modal formulas is denoted as
 ${\mathit {Fm}}$
. Modal logic
 $\mathbf {S4}$
is the smallest set of modal formulas closed under Modus Ponens
 $( \varphi ,\varphi \to \psi /\psi )$
and Necessitation (
 $\varphi /\Box \varphi $
) containing all tautologies of classical logic plus the following schemata of axioms for the modal operator:
 $$ \begin{align*}\begin{array}{|c|c|} (K) & \Box(\varphi\to\psi)\to(\Box\varphi\to\Box\psi) \\ (T) & \Box\varphi\to\varphi \\ (4) & \Box\varphi\to\Box\Box\varphi \\ \end{array}\end{align*} $$
The modal logic
 $\mathbf {S4.1.2}$
contains an additional axiom
 $\Box \Diamond \varphi \leftrightarrow \Diamond \Box \varphi .$
2.1 Topological semantics
Definition 2.2. ([Reference Benthem, Bezhanishvili, Aiello, Pratt-Hartmann and Van Benthem17, Definition 5.1])
Let
 $\langle {X,\tau } \rangle $
be a topological space. A topological model
 $\mathrm {M}$
on
 ${X}$
is a tuple
 $\langle { {X},\tau , \Vdash }\rangle $
, where ⊢ is a relation between elements of X and modal formulas which, for every
 $x\in X$
and formulas
 $\varphi , \psi \in {\mathit {Fm}}$
, satisfies:
-
(i) x ⊢ φ ∨ ψ if and only if x ⊢ φ or x ⊢ ψ.
-
(ii)
 $x\Vdash \neg \varphi $
if and only if
$x\not \Vdash \varphi $
.
-
(iii)
$x\Vdash \Box \varphi $
if and only if
$\exists U\in \tau \, (x\in U\wedge \forall y\in U: y\Vdash \varphi )$
.


From the above and the definition of the connectives we also have:
-
(iv) x ⊢ φ ∧ ψ if and only if x ⊢ φ and x ⊢ ψ.
-
(v) x ⊢ φ → ψ if and only if
$x\not \Vdash \varphi $
or x ⊢ ψ. -
(vi)
$x\Vdash \Diamond \varphi $
if and only
$\forall U\in \tau \, (x\in U\to \exists y\in U: y\Vdash \varphi )$
.


We say that a modal formula
 $\varphi $
is valid in
 $\mathrm {M}$
(or that M satisfies
 $\varphi $
) if for every
 $x\in X$
,
 $x\Vdash \varphi $
. Moreover, we say that
 $\varphi $
is valid in a topological space
 $ X$
if it is valid in every model on
 $ X$
. Finally, we say
 $\varphi $
is valid in a class of topological spaces
 $\mathsf {K}$
, whenever it is valid in every space
 $ X$
from
 $\mathsf {K}$
.
Remark. We deviate slightly from [Reference Benthem, Bezhanishvili, Aiello, Pratt-Hartmann and Van Benthem17] in that ⊢ is not defined from a valuation of the variables (atoms) but it is given directly and expected to satisfy the defining axioms (i–iii).
Remark. Given a topological model
 $\langle {X,\tau ,\Vdash }\rangle $
, let
 $||\varphi ||={\{{x\in X}\,|\,{x\Vdash \varphi }\}}$
. It is easy to see that
 $||\Box \varphi ||=\mathrm {int}(||\varphi ||)$
and
 $||\Diamond \varphi ||=\overline {||\varphi ||}$
. In other words
 $\Box $
is interpreted as the topological interior operation and
 $\Diamond $
as the closure operation (see [Reference Benthem, Bezhanishvili, Aiello, Pratt-Hartmann and Van Benthem17, Section 2.3]).
Definition 2.3. We say that a logic L is (sound and) complete with respect to a class of spaces if
 $\mathbf {L}$
is the set of formulas valid in the class.
Before we state the basic completeness result for
 $\mathbf {{S4}}$
and
 $\mathbf {{S4.1.2}}$
we first need to introduce the notion of a tree and some standard notation.
Definition 2.4. A set T together with a partial order ≤ is a tree if {s ∈ T: s ≤ t} is well-ordered by ≤ for every t ∈ T. Elements of the tree are called nodes. The height of a node t ∈ T, denoted ht(t), is the order type of {s ∈ T: s ≤ t & s ≠t}. Given s ∈ T we write succ
T
(s) = {t ∈ T: s ≤ t & ht(t) = ht(s) + 1} for the set of immediate successors of s in T and T
s
= {t ∈ T: s ≤ t} for the set of “descendants” of s (note that contrary to common usage T
s
does not include the predecessors of s). Recall that a quasi-order
 $\langle {T,\leq }\rangle $
is called a quasi-tree if the canonical quotient order of
 $\langle {T,\leq }\rangle $
is a tree.
Notation. We denote by T (resp.
 $\mathsf {T}^{*}$
) the class of all finite trees (resp. finite trees with an additional top element
 $*$
) regarded as topological spaces with the topology given by upward closed sets in the tree order. The notation QT (resp.
 $\mathsf {QT}^{*}$
) stands for the analogous classes corresponding to quasi-trees instead of trees.
The next result is well-known, for more details see e.g., [Reference Bezhanishvili and Harding5, Proposition 2.5].
Proposition 2.5. The modal logic
 $\mathbf {S4}$
(resp.
 $\mathbf {S4.1.2}$
) is complete with respect to the class
 $\mathsf {QT}$
(resp.
 $\mathsf {QT}^{*}$
).
For more information on topological semantics for modal logics see [Reference Aiello, Benthem and Bezhanishvili1] or [Reference Benthem, Bezhanishvili, Aiello, Pratt-Hartmann and Van Benthem17].
2.6 The interior map strategy
We describe a general method (the interior map strategy) which can be used to obtain new completeness results with respect to topological spaces from already existing ones (e.g., that
 $\mathbf {S4}$
is complete with respect to the Cantor space
 $\mathbb {C}$
or the real line
 $\mathbb {R}$
, see [Reference Aiello, Benthem and Bezhanishvili1]).
Recall that a function between two topological spaces is called an interior map if it is both continuous and open. It is not hard to prove that interior maps preserve topological consequence:
Proposition 2.7 (cf. [Reference Gabelaia7])
Let f be an interior map from
 ${X}$
onto
 ${Y}$
. Then every modal formula
 $\varphi $
is valid in
 $ Y$
, whenever it is valid in
 $ X$
.
To prove a completeness result we typically need to show that if a formula is not valid, then there is a model which serves as a counterexample. The above proposition allows us to transfer counterexamples from one space to another. This is the idea of the interior map strategy.
2.8 The space βω
Recall that the space βω, the Čech–Stone compactification of the countable discrete space ω, can be naturally identified (via Stone duality), with the set of all ultrafilters on ω. The topology is given by basic (cl)open sets of the form
 $$ \begin{align*} \widehat{A} = \{\mathcal{U}\in \beta \omega: A \in \mathcal{U}\}, \end{align*} $$
for some set A ⊂ ω. The space is a
 $T_2$
, compact, extremally disconnected, zero-dimensional, topological space. The subspace consisting of all nonprincipal ultrafilters is denoted
 $\omega^{*}$
. It is a
 $T_2$
, compact zerodimensional space homeomorphic to the Stone space of the algebra
 $\mathcal {P}$
(ω)/fin.
2.9 Almost disjoint families
Almost disjoint families will be the main tool in our construction of an interior map. Here we collect some basic facts about them (for more information, see, e.g., [Reference Hrušák11]).
Definition 2.10. (Folklore)
A family
 $\mathcal {A}$
of infinite subsets of
 $\omega $
is called an almost disjoint family on
 $\omega $
(AD for short) if |A ∩ B| < ω for each A, B ∈
 $\mathcal {A}$
. An infinite maximal (w.r.t. inclusion) AD family is called a maximal almost disjoint family (MAD for short). An AD/MAD family on some other countably infinite X is defined similarly.
Given an AD family
 $\mathcal {A}$
we denote by
 $\mathcal {I} (\mathcal {A})$
the ideal on ω generated by sets in
 $\mathcal {A}$
together with all finite sets. It is natural to ask what are the possible sizes of a MAD family. It is not hard to see that every MAD family must be uncountable and have size at most c. The minimal possible size of a MAD family
 $$ \begin{align*} \mathfrak a = \min\{|\mathcal A|:\mathcal A\ \mbox{is a MAD family}\} \end{align*} $$
is called the almost disjoint number. It can consistently be strictly smaller than
 $\mathfrak {c}$
. However, MAD families of size
 $\mathfrak {c}$
always exist. To see this consider the family of branches of the full binary tree of height ω. This is clearly an AD family (on the countable set of nodes of the binary tree) of size
 $\mathfrak {c}$
. Then, by the axiom of choice, it can be extended to a MAD family.
In our main construction we will be relying on the following concept:
Definition 2.11. [Reference Hechler9]
An AD family
 $\mathcal {A}$
is completely separable if for every X∉
 $\mathcal {I}(\mathcal {A})$
either X is almost disjoint with each element of
 $\mathcal {A}$
or there is A ∈
 $\mathcal {A}$
such that A ⊂* X (recall that A ⊂* X means that |A ∖ X| < ω).
Notice that if
 $\mathcal {A}$
is a MAD family then the first alternative cannot hold. It is also not hard to see that in the second alternative we can equivalently require that the set of such As has size continuum [Reference Hrušák and Simon12].
A completely separable MAD family will be instrumental in our proof. While it is easy to construct a completely separable AD family by transfinite recursion, it is a long-standing open question whether there is, in ZFC, a completely separable MAD family. Their existence easily follows from
 $\mathfrak {a=c}$
. Recently (see [Reference Shelah14], and others), they have been shown to exist under various much weaker assumptions, e.g., if
 $\mathfrak {c}$
≤ ℵ
ω
, but it is conceivable, that their existence is outright provable in ZFC. For more on this topic see, e.g., the survey paper [Reference Hrušák and Simon12].
Finally, we finish with a simple technical lemma, which will be important in the next section.
Lemma 2.12. Assume A is an infinite AD family of infinite subsets of X ⊂ ω. Then the set
 $$ \begin{align*} Z=\omega^*\cap\widehat{X}\setminus\bigcup\left\{\widehat{A}:A\in\mathcal A\right\} \end{align*} $$
is a compact subspace of
 $\omega^{*}$
without isolated points.
Proof. The set is closed (and
 $\omega ^*$
is
 $T_2$
) and hence compact. To see that it has no isolated points let p ∈ Z and B^ a neighbourhood of p (in
 $\omega ^*$
). We will show that
 $|\widehat {B}\cap Z|>1$
. There are two cases. Either
 $$ \begin{align*} p\not\in\overline{\bigcup\left\{\widehat{A}:A\in\mathcal A\right\}}. \end{align*} $$
Then there must be a C ∈ p such that C is almost disjoint from A. Then
 $ \widehat{B}\cap \widehat {C} \cap \widehat{X} \cap \omega ^{*} \subseteq Z \cap \widehat{B}$
is a clopen neighbourhood of p in ω
* so, in particular, it has size
 $\mathfrak c > 1$
.
Dealing with the second case assume that
 $$ \begin{align*} p\in\overline{\bigcup\left\{\widehat{A}:A\in\mathcal A\right\}}\setminus\bigcup\left\{\widehat{A}:A\in\mathcal A\right\}. \end{align*} $$
It follows that B can’t be almost disjoint from
 $\mathcal {A}$
and can’t be almost covered by finitely many elements of
 $\mathcal {A}$
either. In particular B has to intersect infinitely many elements of
 $\mathcal A$
in an infinite set. Choose such an infinite family
 $\{ A_n : n < \omega \} \subseteq \mathcal {A}$
and, for each n, let
 $ B_n^{\prime} = B \cap A_n $
be the (infinite) intersection.
Next, make the sets disjoint
 $$ \begin{align*} B_n=B^\prime_n\setminus\bigcup\limits_{i<n}B^\prime_i \end{align*} $$
and partition each B n into two disjoint infinite subsets C n and D n . Let
 $$ \begin{align*} C=\bigcup\limits_{n<\omega} C_n,\quad D=\bigcup\limits_{n<\omega}D_n. \end{align*} $$
Then C, D ⊂ X ∩ B (recall that
 $A\subseteq X$
for each
 $A\in \mathcal A$
and, hence, also
 $C,D\subseteq X$
) are disjoint so at most one can be an element of p. Without loss of generality assume that C ∉ p. Notice that C cannot be almost covered by finitely many elements of
 $\mathcal {A}$
(because it hits each A
n
in an infinite set and
 $\mathcal {A}$
is almost disjoint) so
 $$ \begin{align*} \widehat{C}\cap Z=\widehat{C}\setminus\bigcup\left\{\widehat{A}:A\in\mathcal A\right\}\neq\emptyset. \end{align*} $$
In particular there is
 $q\in \widehat {C}\cap \widehat {Z}\subseteq Z\cap \widehat B$
with
 $q\neq p$
. So
 $ | \widehat{B} \cap Z | \geq 2 $
.
Since
 $ \widehat{B}$
was an arbitrary clopen neighbourhood of p this finishes the proof that p is not isolated in Z.⊣
3 The interior map construction
The aim of this section is to prove the following theorem:
Theorem 3.1. Assume there is a completely separable MAD family. Then for every
 $T\in \mathsf {T}^{*}$
there is a surjective interior map f from
 $\beta \omega $
onto T.
Before we present the proof we shall illustrate the idea of the construction on an example of 3-element tree
 $T_1$
and then we extend the construction to a 6-element tree
 $T_2$
demonstrating the level-based procedure.

To obtain a surjective interior map from
 $\beta \omega $
onto the tree
 $T_1$
consider
 $\mathcal A$
, a completely separable MAD family on
 $\omega $
. Partition each element
 $A\in \mathcal A$
into two pieces
 $A_1$
and
 $A_2$
and denote the collection of all of them as
 $\mathcal A_1$
and
 $\mathcal A_2$
respectively. Our map sends points from
 $\omega $
onto the top element
 $*$
, those from
 $\widehat { \mathcal A_1 }(= \bigcup \{\widehat {A}:A\in \mathcal A_1\})$
to
 $s_2$
, those from
 $\widehat {\mathcal A_2}$
to
 $s_3$
and the remaining ones to
 $s_1$
. Such a map is clearly surjective and continuous. To see that it is open, we crucially use the fact that
 $\mathcal A$
is completely separable: indeed, assume that
 $p\in \widehat X$
is sent to
 $s_1$
for some infinite X. Then, it must be the case that
 $X\not \in \mathcal I(\mathcal A)\supseteq \mathcal I(\mathcal A_1)\cup \mathcal I(\mathcal A_2)$
. Consequently, there is
 $A\in \mathcal A$
such that
 $A\subseteq ^*X$
. Then the ultrafilters from
 $\widehat A_1$
and
 $\widehat A_2$
show that
 $s_2,s_3\in f[\widehat {X}]$
and the isolated ultrafilters in
 $\widehat {X}$
show that
 $*\in f[\widehat {X}]$
, so
 $f[\widehat {X}]$
is open.

The second map will agree with the previous one on the preimages of
 $s_1$
and
 $s_2$
. We only redistribute the preimage of
 $s_3$
into the succeeding nodes similarly as we have seen before. To this end, for every
 $A\in \mathcal A_2$
, we pick a completely separable MAD family
 $\mathcal B^A$
on A and partition each of its elements into three pieces (corresponding to the nodes
 $s_4$
,
 $s_5$
, and
 $s_6$
) and we collect them into
 $\mathcal B^A_4$
,
 $\mathcal B^A_5$
, and
 $\mathcal B^A_6$
. The new map is redefined to send, for every
 $A\in \mathcal A_2$
, the elements from
 $\widehat {\mathcal B^A_i}$
to the corresponding node
 $s_i$
,
 $i=4,5,6$
. The remaining ones from
 $\widehat {\mathcal A_2}$
are still sent to
 $s_3$
.
The construction for an arbitrary tree is just a more elaborate version of the above idea.
Proof of Theorem 3.1
Consider a finite tree T with an additional top element
 $\ast $
. First for every node
 $t\in T$
we recursively construct a nonempty almost disjoint family
 $\mathcal A_t$
as follows.
For the root r we put
 $\mathcal A_r=\{\omega \}$
. Suppose
 $\mathcal A_t$
is already defined for
 $t\in T$
. For every
 $A\in \mathcal A_t$
let
 $\mathcal A^A$
be a completely separable MAD family on A which exists by our assumption. Partition each element B of
 $\mathcal A^A$
into
 $|succ_T(t)|$
-many pieces
 $B=\bigcup _{s\in succ_T(t)}B_s$
and denote
 $\mathcal A^A_s={\{{B_s}\,|\,{B\in \mathcal A^A}\}}$
for
 $s\in succ_T(t)$
. Finally define
 $$\begin{align*}\mathcal A_{s}=\bigcup\limits_{A\in \mathcal A_t}\mathcal A_s^A.\end{align*}$$
It can easily be seen that for every
 $s,t\in T$
the construction ensures:
 $$ \begin{align} &\quad\mbox{If } s\leq t, \mbox{ then for every } A\in\mathcal A_t \mbox{ there is } A'\in \mathcal A_s \mbox{ such that } A\subseteq A'. \end{align} $$
 $$ \begin{align} &\quad\mbox{If } t\nleq s \mbox{ and } s\nleq t, \mbox{ then } \mathcal A_s\cup\mathcal A_t \mbox{ is an AD family.} \end{align} $$
In the remaining part of the proof, if
 $\mathcal A$
is an AD family, we write
 $\widehat {\mathcal A}=\bigcup _{A\in \mathcal A}\widehat A $
. For every
 $t\in T$
we define a collection of nonprincipal ultrafilters
 $\mathcal B_t\subseteq \omega ^\ast $
recursively as follows. If t is a leaf of T let
 $\mathcal B_t=\widehat { \mathcal A_t}$
, otherwise let
 $$ \begin{align} \mathcal B_t=\widehat {\mathcal A_t}\setminus \bigcup\limits_{s\in succ_T(t)}\widehat{\mathcal A_s}. \end{align} $$
Claim 3.2.
 $$ \begin{align*} \mathcal B_t=\bigcup\limits_{A\in \mathcal A_t}\widehat A\setminus \widehat{\mathcal A^A}. \end{align*} $$
Proof of Claim. First notice that,
 $$ \begin{align*} \bigcup\limits_{s\in succ_T(t)} \widehat{\mathcal A_s} = \bigcup\limits_{s\in succ_T(t)} \bigcup\limits_{A\in \mathcal A_t} \widehat{\mathcal A_s^A} = \bigcup\limits_{A\in \mathcal A_t} \bigcup\limits_{s\in succ_T(t)} \widehat{\mathcal A_s^A} = \bigcup\limits_{A\in \mathcal A_t} \widehat{\mathcal A^A}, \end{align*} $$
where the last equality follows from the fact that
 $succ_T(t)$
is finite. The claim now easily follows. ⊣
We show that for every
 $s,t\in T$
the following holds:
 $$ \begin{align} & \mbox{If }t\neq s,\mbox{ then } \mathcal B_t\cap \mathcal B_s=\emptyset. \end{align} $$
 $$ \begin{align} & \widehat{\mathcal A_t} = \bigcup\limits_{t\leq u}\mathcal B_u . \end{align} $$
 $$ \begin{align} & \mathcal B_t\neq \emptyset. \end{align} $$
We start with (4). If
 $s,t$
are incomparable the conclusion follows immediately from (2). Otherwise assume, without loss of generality,
 $s<t$
. Then there is
 $u\in T$
such that
 $s<u\leq t$
and
 $u\in succ_T(s)$
. Moreover if
 $p\in \mathcal B_t$
, then there is
 $A\in \mathcal A_t$
such that
 $A\in p$
. By (1) there is
 $A'\in \mathcal A_u$
such that
 $A\subseteq A'$
. Therefore
 $p\in \widehat A'$
and by (3)
 $p\notin \mathcal B_s$
.
We prove (5) by induction on the distance of t to the top node. When t is a leaf node, (5) is just the definition. Suppose now that the claim is true for all
 $s\in succ_T(t)$
. Then
 $$ \begin{align*} \bigcup\limits_{t\leq u}\mathcal B_u= \mathcal B_t\cup \bigcup\limits_{s\in succ_T(t)}\bigcup\limits_{s\leq u}\mathcal B_u = \mathcal B_t\cup \bigcup\limits_{s\in succ_T(t)}\widehat {\mathcal A_s}= \widehat{\mathcal A_t}, \end{align*} $$
where the second equality follows from the inductive assumption and the last from (3).
Finally (6) clearly holds for every leaf node. If t is not a leaf node, then, since for every
 $A\in \mathcal A_t$
the set
 $\widehat A\setminus \widehat {\mathcal A^A}$
is nonempty, Claim 3.2 concludes the proof of (6).
We are now ready to define the desired map
 $f\colon \beta \omega \to T\cup \{\ast \}$
. We let
 $f(p)=\ast $
for all principle ultrafilters p. For nonprincipal p we let
 $$\begin{align*}f(p)=t \quad \Longleftrightarrow\quad p\in\mathcal B_t. \end{align*}$$
Observe that the map f is well defined by (4) and (5). By (5), the map is continuous (note that
 $f^{-1}[T_t]=\bigcup _{t\leq u}\mathcal B_u= \widehat {\mathcal A_t}$
). It is surjective by (6).
Therefore it only remains to show that f is open. That is for every node t we want to show that for every basic open neighborhood
 $\widehat X$
of a nonprincipal ultrafilter p we have that
 $f(p)=t$
implies
 $T_t\subseteq f[\widehat X]$
(clearly always
 $\ast \in f[\widehat X])$
. We prove this by induction on the distance of t to the top. For leaf nodes there is nothing to prove. Thus assume the claim holds for every
 $s\in succ_T(t)$
and consider
 $p\in \widehat X$
such that
 $f(p)=t$
. Since
 $f(p)=t$
, there is
 $A\in \mathcal A_t$
such that
 $A\in p$
. Denote
 $Y=X\cap A$
. Since
 $\mathcal A^A$
is completely separable MAD family on A and
 $Y\notin \mathcal I(\mathcal A^A)$
, there is
 $B\in \mathcal A^A$
such that
 $B\subseteq ^\ast Y$
. Thus for every
 $s\in succ_T(t)$
the set
 $B_s\subseteq B$
belongs to
 $\mathcal A_s$
. Consequently by Claim 3.2, there is an ultrafilter q such that
 $B_s\in q$
and
 $q\in \mathcal B_s$
(equivalently
 $f(q)=s$
). Since
 $B_s\subseteq ^\ast X$
, the induction assumption ensures that
 $T_t\subseteq f[\widehat X]$
.⊣
Corollary 3.3. For every
 $X\in \mathsf {QT}^{*}$
there is a surjective interior map f from
 $\beta \omega $
onto X.
Proof. This is precisely the Main Lemma and Corollary 4.10 from [Reference Bezhanishvili and Harding4]. The idea is the following: let
 $X\in \mathsf {QT}^{*}$
be given. Then there is a projection map
 $\pi $
from X onto its quotient order
 $X/_\approx $
. This projection is an interior map with respect to the corresponding upset topologies. By Theorem 3.1 there is an interior onto map
 $f:\beta \omega \to X/_\approx $
. We prove there is a surjective interior map
 $g\colon \beta \omega \to X$
such that the following commute:

Such a map exists because for each
 $*\neq x\in X/_\approx $
the subspace
 $f^{-1}(x)$
is k-resolvable (i.e. it is a union of k-many disjoint dense subsets) for every natural number k, in particular for
 $k=|\pi ^{-1}(x)|$
. Indeed by applying Claim 3.2 and Lemma 2.12 to the definition of
 $f^{-1}(x)$
, the preimage
 $f^{-1}(x)$
is locally compact and has no isolated points. It is obviously Hausdorff so it is k-resolvable by [Reference Hewitt10, see comments on p. 332]. ⊣
A straightforward modification of the above proofs gives (just restricting the map to
 $\omega^{*}$
whose image is the tree without the top element):
Corollary 3.4. For every
 $X\in \mathsf {QT}$
there is a surjective interior map f from
 $\omega ^*$
onto X.
4 Completeness results
Theorem 4.1. The Modal logic
 $\mathbf {S4.1.2}$
is the logic of the space
 $\beta \omega $
.
Proof. Completeness: suppose
 $\varphi \notin \mathbf {S4.1.2}$
, then, by Theorem 2.5, there is
 $ X\in \mathsf {QT}^{*}$
which refutes
 $\varphi $
. By Corollary 3.3, there is a surjective interior map from
 $\beta \omega $
onto
 $ X$
. Therefore, by Proposition 2.7, we conclude that
 $\varphi $
is not valid in
 $\beta \omega $
.
Soundness: we want to show that every theorem of
 $\mathbf {S4.1.2}$
is valid in
 $\beta \omega $
. Since all theorems of
 $\mathbf {S4}$
are valid in
 $\beta \omega $
, we only need to verify the additional two axioms. The axiom
 $\Box \Diamond \varphi \to \Diamond \Box \varphi $
is valid in every space with a dense set of isolated points (see [Reference Bezhanishvili, Mines and Morandi6]) and the axiom
 $\Diamond \Box \varphi \to \Box \Diamond \varphi $
is valid precisely in extremally disconnected spaces (see [Reference Gabelaia7]). Consequently, both axioms are valid in
 $\beta \omega $
(isolated points of
 $\beta \omega $
are precisely the principal ultrafilters on
 $\omega $
and they are dense in
 $\beta \omega $
). ⊣
Theorem 4.2. The Modal logic
 $\mathbf {S4}$
is the logic of the space
 $\omega ^*$
.
Proof. Completeness follows by essentially the same argument as in the proof of Theorem 4.1: we use Theorem 2.5 and Corollary 3.4.
Soundness follows from the fact that every topological space is sound w.r.t. the modal logic
 $\mathbf {S4}$
. ⊣
5 Conclusion
Let us mention that the completeness results for the modal logic
 $\mathbf {{S4}}$
(and
 $\mathbf {{S4.1.2}}$
, resp.) obtained in this paper translate into completeness results for intutionistic logic (and, resp., the Jankov’s logic
 $\mathbf {{KC}}$
—i.e. intuitionistic logic + the axiom of weak excluded middle
 $\neg \varphi \vee \neg \neg \varphi $
). For more details see [Reference Bezhanishvili and Harding4]. The results can also be used to weaken the assumptions of many results from [Reference Bezhanishvili and Harding5], where the authors discuss the logics of Stone spaces in general. For other topological completeness results for modal logics see, e.g., [Reference Bezhanishvili, Bezhanishvili, Lucero-Bryan and van Mill3, Reference Mill, Bezhanishvili, Lucero-Bryan and Bezhanishvili19].
Our proof of the main Theorem 3.1 assumed the existence of completely separable MAD families. Naturally, we tried to prove the result avoiding the additional assumption. Unfortunately, we only have partial results in this direction: we know that Theorem 3.1 holds for trees of height
 $2$
without additional assumptions—the proof is analogous but in this case it is enough to consider k-partitionable MAD families, which are known to exists in ZFC [Reference Douwen18]; the theorem also holds for all finite binary trees (though with a very different proof using the fact, due to B. Balcar and P. Vojtáš [Reference Balcar and Vojtáš2], that every ultrafilter has an almost disjoint refinementFootnote
1
). Unfortunately, the argument does not extend to infinite binary trees (which, as was pointed out to us by the referee, would be enough since
 $\mathbf {S4}$
is complete w.r.t. the infinite binary tree by a result of Gabbay and van Benthem; see [Reference Goldblatt8]).
Of course, if it turns out that completely separable MAD families exist in ZFC, our construction will be a ZFC construction.
Acknowledgment
The research of the first author was supported by project no. GA17-04630S of the Czech Science Foundation. The research of the second author was supported by FWF-GAČR grant no. 17-33849L: Filters, Ultrafilters and Connections with Forcing and by Charles University Research Centre program No. UNCE/SCI/022



